A data request is the most direct privacy check you can run. Rather than reading a policy about what a company might do with your information, you get a copy of what it actually holds.
Which rules apply to you
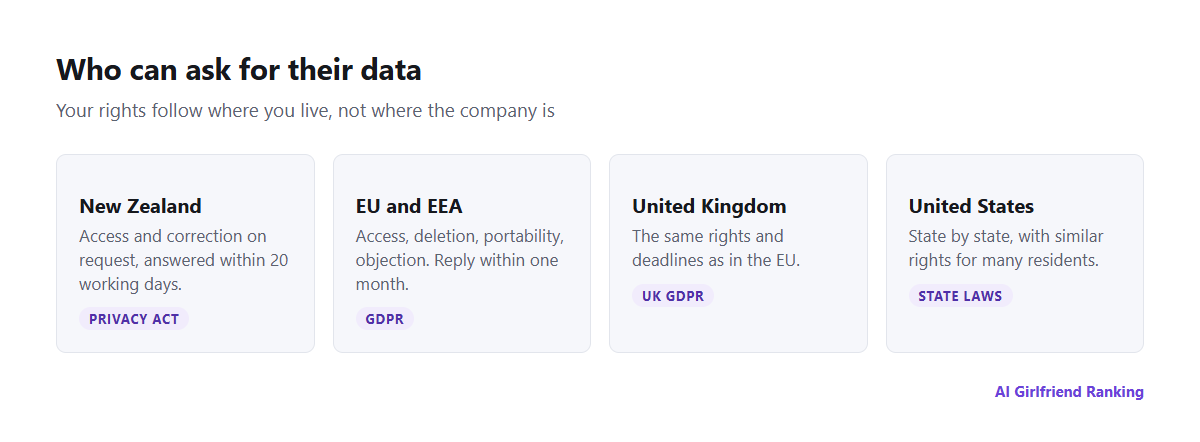
Your rights follow where you live, not where the company keeps its servers.
- New Zealand: the Privacy Act 2020 and its Information Privacy Principles. Principle 6 gives you access to the personal information an organisation holds about you, and you can ask for it to be corrected. Whether a small overseas startup answers is another matter.
- EU and EEA: GDPR adds a right to delete and export your data, and to object to certain uses. It applies if the company offers its service to people in Europe.
- UK: UK GDPR, with the same rights.
- US: state laws such as California's CCPA give US residents comparable rights. They matter for you mostly as context, since you would be relying on the New Zealand Act.
Even if a company says none of these bind it, ask anyway. Many handle every request the same way because that is easier than sorting people by country.
A caution on deletion. The Privacy Act 2020 is built around access and correction, not a GDPR-style "right to erasure". Organisations should not keep information longer than they need it, and you can still ask. Some will say yes simply because it is their policy.
Choosing what to ask for
| What you want | What you receive | Best moment |
|---|---|---|
| Access | A copy of your information and how it is used | Always the first request |
| A portable copy | Your data in a format another service can read | Before moving to a different app |
| Deletion | Your information destroyed or de-identified | Leaving for good, or after a breach |
| Stop certain uses | No more model training or marketing use | Sticking around on your terms |
| Correction | Wrong details fixed | Incorrect age or email, mixed-up accounts |
A message you can paste
Send it from the email address tied to your account. Aim it at the privacy contact in the company's policy (often privacy@ or dpo@), or use its privacy form. You do not have to say it is a formal request under a particular law, but naming one helps.
Subject: Request for access to my personal information

I am asking for access to the personal information you hold about me under Information Privacy Principle 6 of the Privacy Act 2020 (and Article 15 GDPR where it applies). My account email is [address] and my username is [username].

Please send: a copy of everything you hold about me, including chat history, images I made or uploaded, voice recordings, memory or profile data inferred from my chats, payment records and device data; why you hold it; who you have passed it to, including advertisers and AI model providers; how long you keep it; and whether it has been used to train or improve AI models.

Please reply within 20 working days, and tell me if you intend to charge a fee.
To ask for deletion instead, swap the first paragraph for a request to delete all your personal information and to confirm in writing when that is done, backups and service providers included.
Signs of a good reply
A conscientious company sends a downloadable archive: your chats, a list of the stored "memories" about you, images, billing and login history, and a plain explanation of who received what. Look hardest at two parts:
- Inferred data. Summaries, personality notes and "facts about you" the app worked out itself. These are frequently the most revealing pages, and they show how AI companion memory works for you in particular.
- Recipients. Model providers, analytics firms and ad partners. Set the list against what the privacy policy claimed; the background is in do AI girlfriend apps sell your data.
If you are ignored or stonewalled
- Follow up in writing once 20 working days have passed, quoting the date of your first message.
- Lodge a complaint with the company about how it handled the request. Start with the company's privacy officer; the Privacy Commissioner expects you to have done this first.
- Go to the Privacy Commissioner. If the company has not answered within 20 working days, or you are unhappy with its response, you can complain to the Office of the Privacy Commissioner (OPC) through its online form, after its short self-assessment. The OPC can investigate, settle and direct access.
- Keep every message and date. Regulators ask for them.
Regulators do act in this space. Italy's data protection authority fined the company behind Replika 5 million euros in 2025, partly because its privacy policy did not clearly explain what it did with people's data.
Export before you erase
If you might want your character or chat history one day, download it or run the app's export tool before asking for deletion. Deletion cannot be undone, and some apps only rotate backups out after several weeks. The full order of steps is in deleting an AI companion account.
Worth doing even if you stay
A data request doubles as a quiet character test. A company that answers clearly and on time is showing you how it treats the rest of your information. One that goes silent is telling you something too, and you will have found out before a breach rather than after it.